Services
Three core services that make security work solid — from asset inventory to penetration validation.
Security services
Three core services, each following the same delivery process and standards
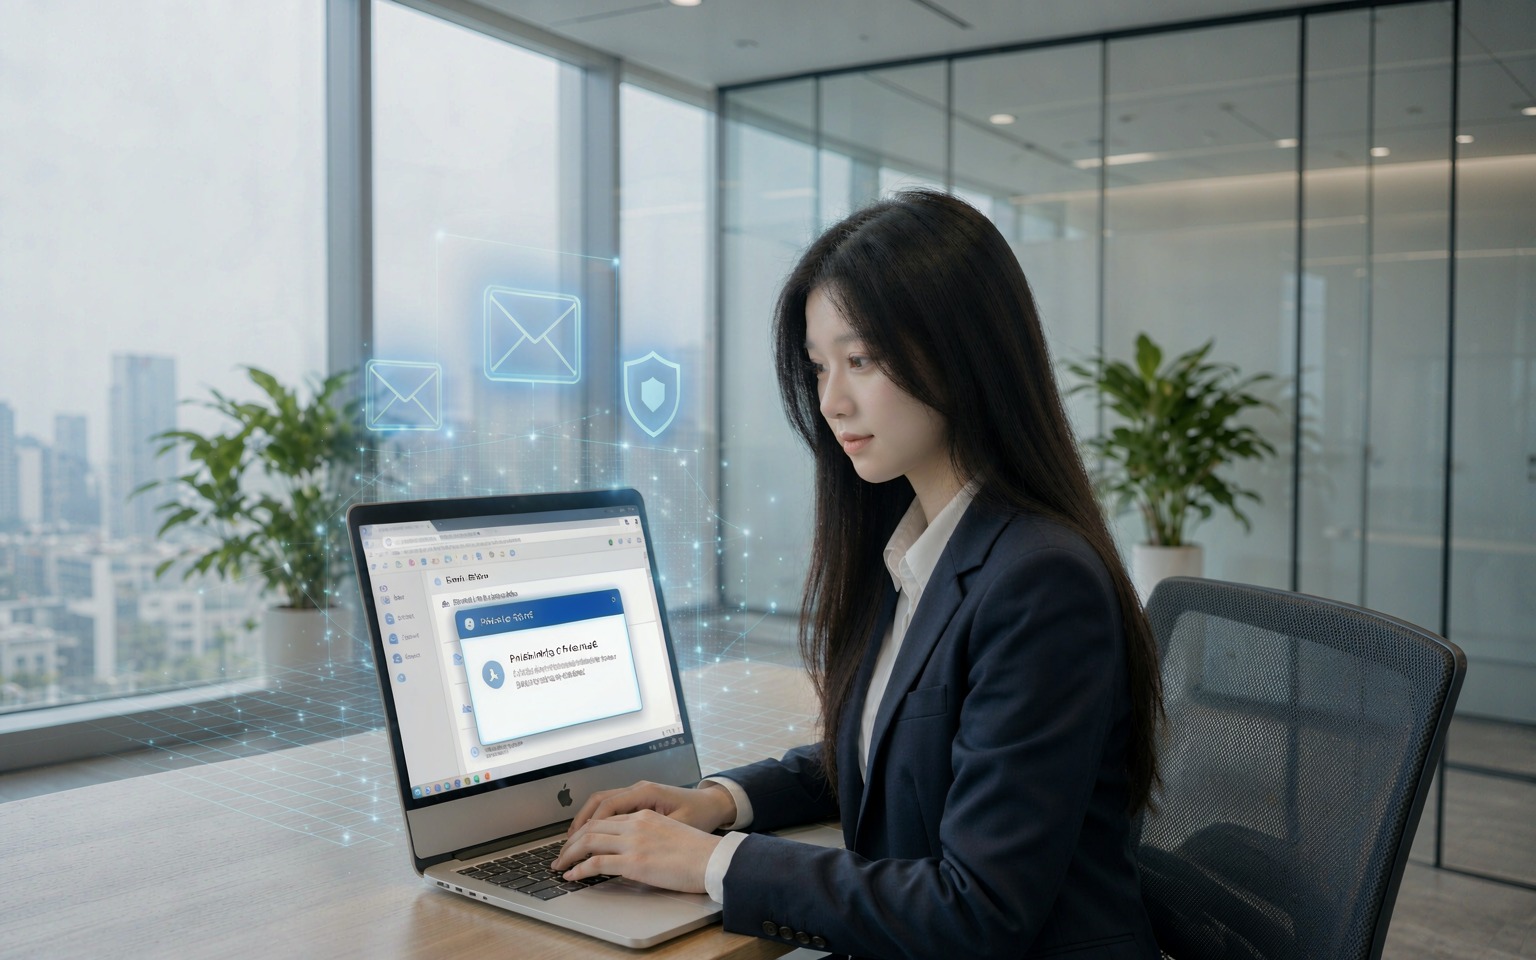
Phishing email exercise
Test how your team really reacts with realistic simulated emails, and turn security awareness from a slogan into data.
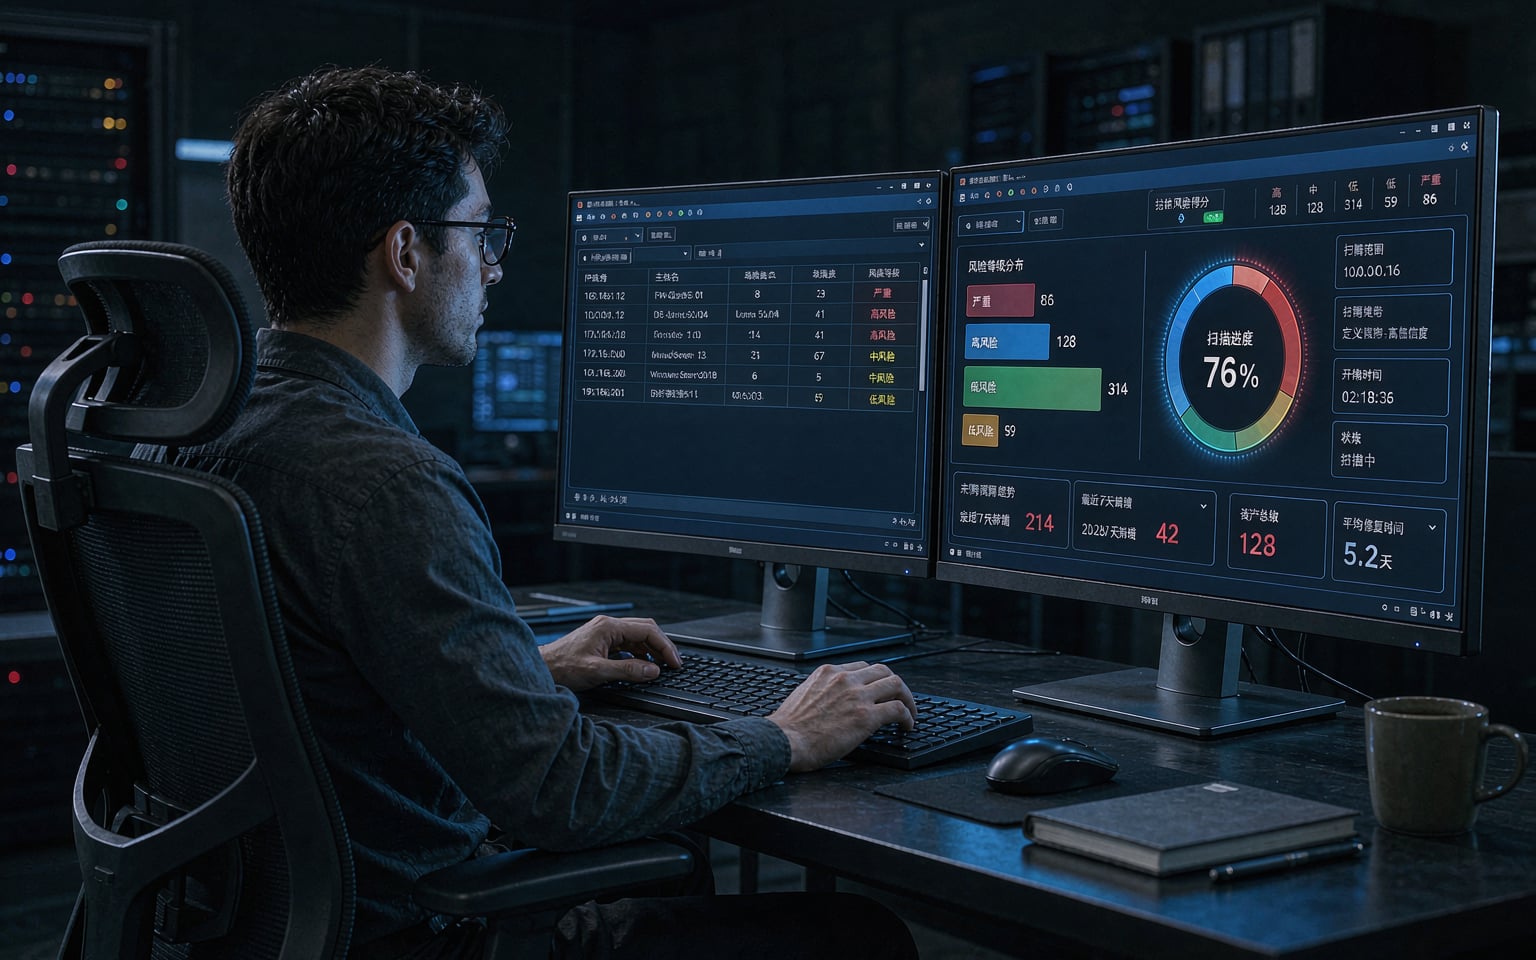
Vulnerability assessment
Understand your assets first, then talk about vulnerabilities — scanning is only the starting point; manual review is what produces conclusions.
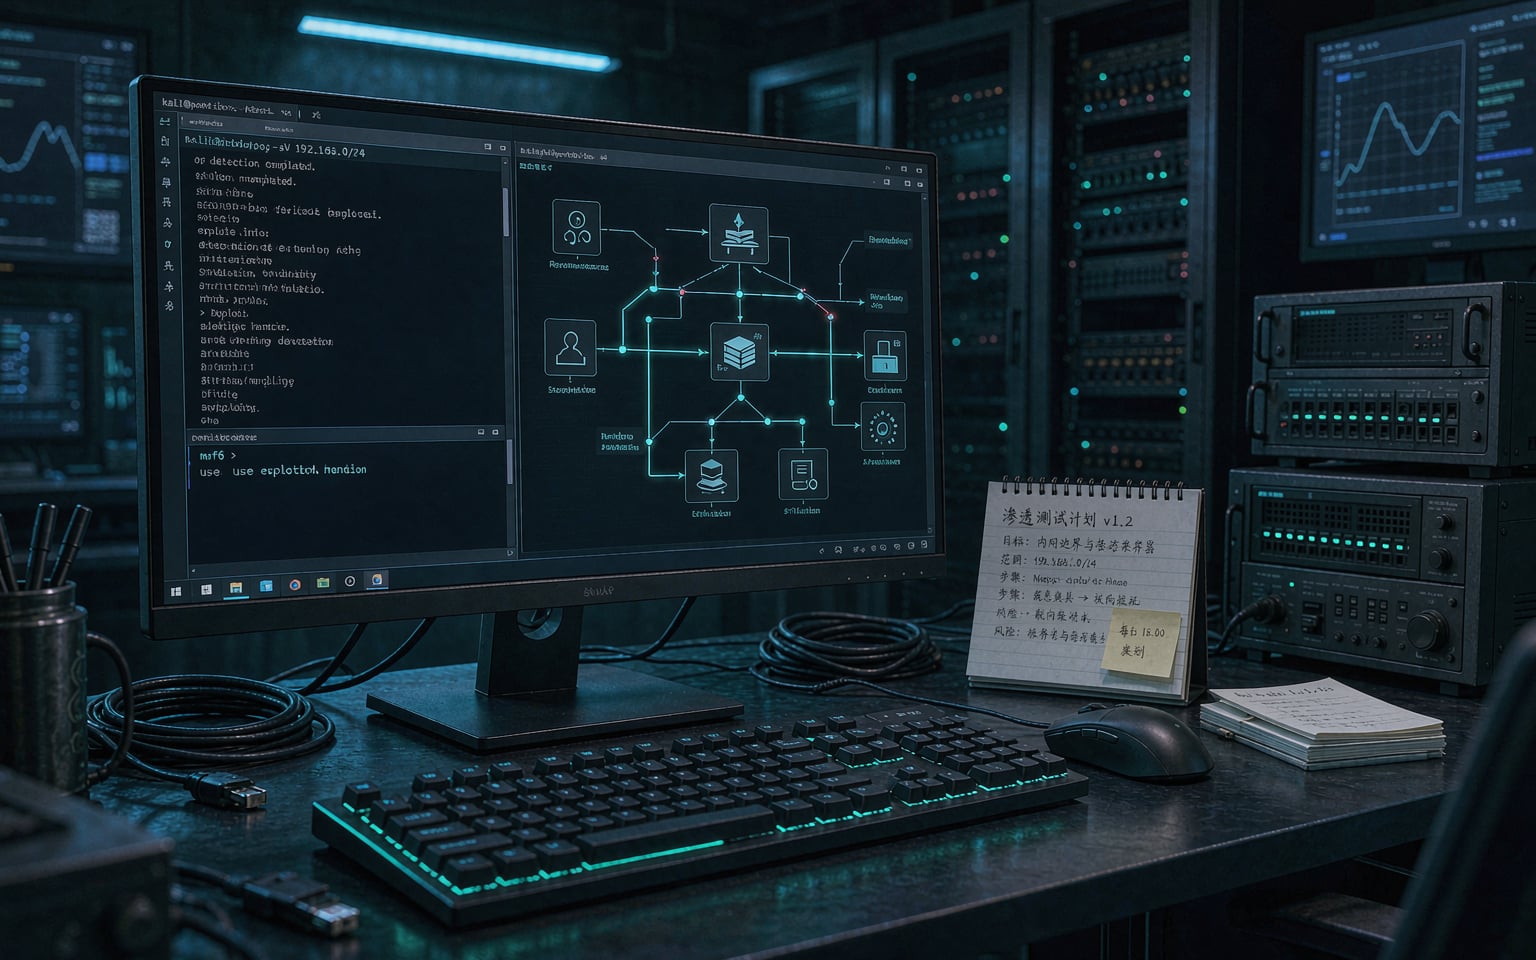
Penetration testing
Taking the attacker perspective, verify whether vulnerabilities can really be exploited — and how deep an attacker can go.
Methodology
Every service follows the same verifiable delivery process
Confirm scope and authorisation
Agree objectives, scope and authorisation, plus the time window and deliverables.
Asset review and information gathering
Map assets and exposure, then set the targets and priorities for testing.
Testing execution and behaviour logging
Run testing and validation as planned, keeping a full record throughout.
Result analysis and risk rating
Manual review removes false positives and rates findings by risk level.
Report delivery and retest verification
Deliver a structured report with actionable remediation and a retest plan.