Phishing email exercise
With authorisation in place we design multiple rounds of simulated emails based on your real business scenarios, covering malicious attachments, lure links and spoofed login pages. The exercise only records behaviour and never collects real credentials: we measure open, click, submission and reporting rates, build a risk profile by department and role, run one targeted awareness session, then retest with equally difficult scenarios to verify that improvement actually happened.
What is included
- Email scenarios and messaging tailored to your business
- Send in batches to control impact
- Risk profiles by department and role
- Retest at equal difficulty after training to verify improvement
Process
1Confirm scope and authorisation
2Scenario and messaging design
3Batched delivery and behaviour logging
4Data analysis and risk profiling
5Training, retest and improvement advice
Ask about this service
Vulnerability assessment
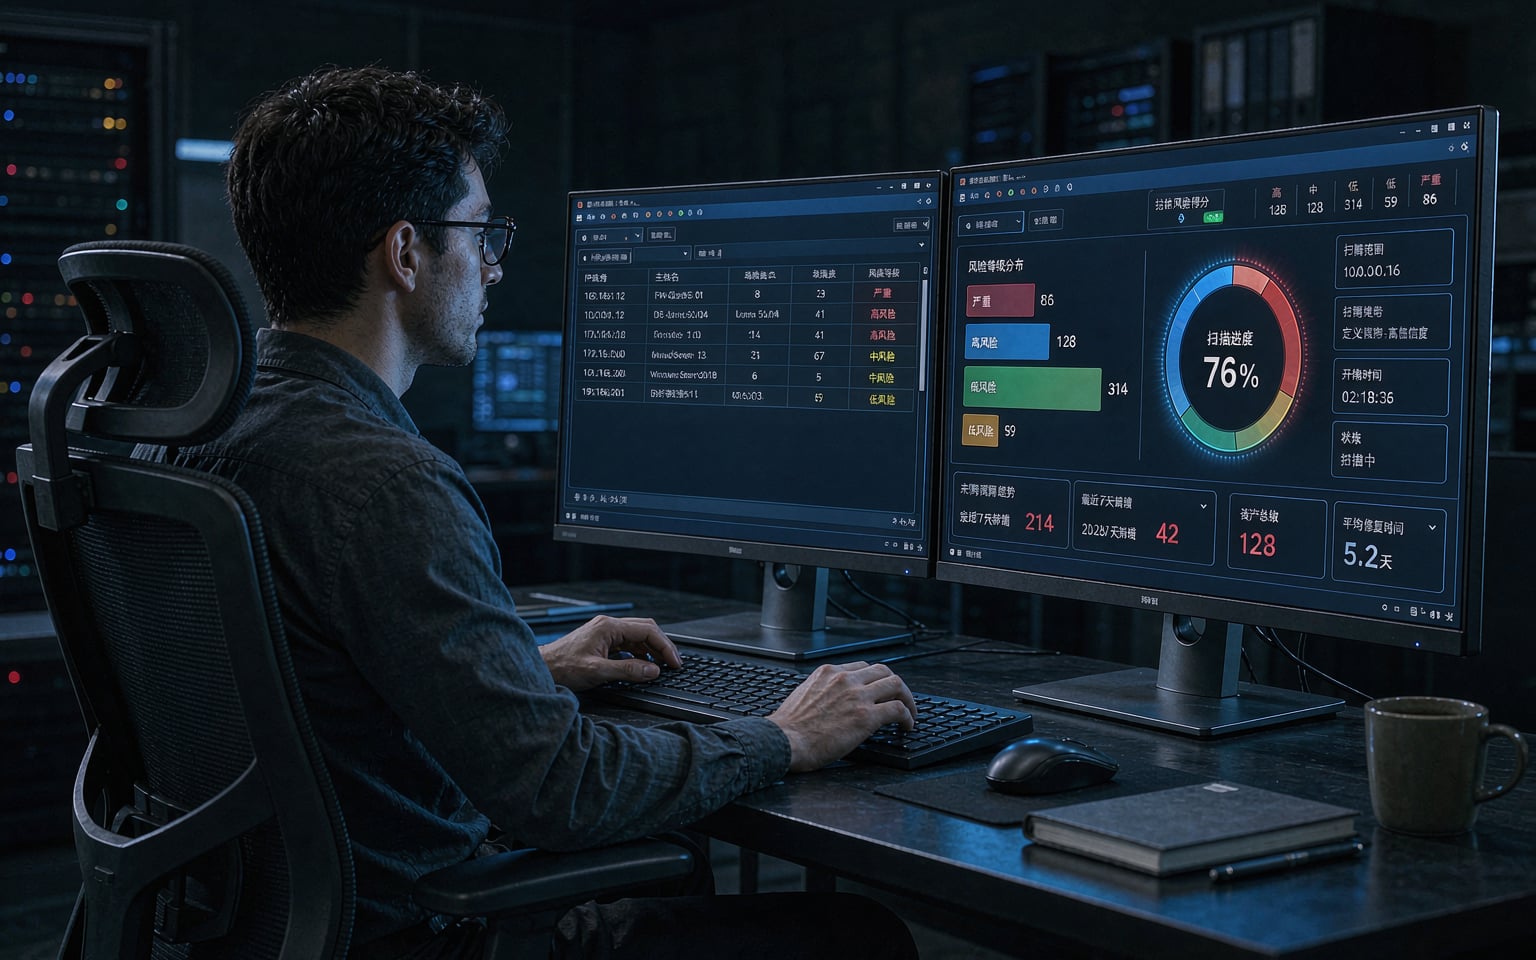
We start with asset inventory: registering domains, IPs, ports, systems and middleware one by one to build a maintainable asset register. Automated tooling then covers the full asset base, after which engineers manually review every finding — removing false positives, confirming genuinely exploitable high-risk issues, rating them by exploitability and impact, and providing directly actionable fixes and hardening advice. What we deliver is a verified conclusion, not a raw scanner export.
What is included
- Asset register review and exposure confirmation
- Full coverage with automated detection tooling
- Line-by-line manual review to remove false positives
- Rate by exploitability and provide fixes
Process
1Asset review and scope confirmation
2Automated detection execution
3Manual review of results
4Risk rating and remediation advice
5Report delivery and retest
Ask about this service
Penetration testing
Within a written authorisation and an agreed time window, we test web applications, mobile apps, hosts and internal networks from the attacker perspective: from information gathering and perimeter breach to privilege escalation and lateral movement, replicating real attack paths to verify whether each vulnerability is genuinely exploitable and how far it can be taken. The whole process is fully logged. Afterwards we deliver a report by risk level with reproduction steps and remediation advice, and schedule a retest once fixes are complete to confirm the risk is truly closed.
What is included
- Tailor test strategy and time window to the target
- Exploit validation and authenticity verification
- Findings presented by risk level with impact
- Retest after remediation to confirm the risk is closed
Process
1Authorisation confirmation and scope definition
2Information gathering and asset review
3Vulnerability validation and deeper exploitation
4Process logging and risk rating
5Report delivery and retest verification
Ask about this service